Introduction
There has recently been an attack on several PeerTube instances utilising a vulnerability (now patched in v8.1.6) which allowed a threat actor to gain control of the root account.
This blog post aims to to notify users of peertube.tech regarding the incident, detail the attack process, and explain how to detect and remediate the attack for other instance owners.
Abstract
Please note that the following is a summary of what happened to the PeerTube Tech instance. Check with your own instance administrators for their situation. For general advice to PeerTube instance owners, go to this section for more information.
No user data was affected on PeerTube Tech, and no dangerous code was executed. While the attacker did gain access, they didn’t affect anything of importance. PeerTube Tech has been updated to v8.1.7 which includes the patch to this vulnerability.
Backstory
- (UTC) Wednesday, May 20th at 9:36am: The PeerTube version 8.1.6 was released. It describes that two security vulnerabilities were fixed. This alerted PeerTube Tech of the issue initially.
- (UTC) Wednesday, May 20th: PeerTube Tech was updated to v8.1.6.
- (UTC) Saturday, May 23rd at 12:19am: A user (who I will not name in interest of privacy) discussed in the PeerTube Matrix chat how a threat actor installed an unknown plugin on their PeerTube instance. This was when PeerTube Tech’s logs were investigated.
Timeline
Summary
- 19/05/2026, 04:43:14: The attacker started targeting PeerTube Tech.
- 21/05/2026, 05:17:57: The attacker gained access to the root account.
- 23/05/2026, 06:47:45: The attacker installed a plugin that didn’t run any dangerous code.
- 23/05/2026, 06:47:47: The attacker was removed from the system.
Detailed
The attacker requested information regarding PeerTube Tech:
info[19/05/2026, 04:43:14] 20.240.202.159 - - [18/May/2026:18:43:14 +0000] "GET /api/v1/config HTTP/1.1" 200 11646 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
They then kept testing if they have gained access to the root account, starting with this log:
info[19/05/2026, 04:50:08] 20.240.202.159 - - [18/May/2026:18:50:08 +0000] "GET /api/v1/users/me HTTP/1.1" 401 157 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
This continued over the span of 2 days until they gained access. Notice how they received a 200 OK code in the second log:
info[21/05/2026, 05:17:48] 20.240.202.159 - - [20/May/2026:19:17:48 +0000] "GET /api/v1/users/me HTTP/1.1" 401 157 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
info[21/05/2026, 05:17:57] 20.240.202.159 - - [20/May/2026:19:17:57 +0000] "GET /api/v1/users/me HTTP/1.1" 200 2061 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
Once they had access, they installed a malicious plugin:
info[23/05/2026, 06:47:45] 20.240.202.159 - - [22/May/2026:20:47:45 +0000] "POST /api/v1/plugins/install HTTP/1.1" 200 389 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
The plugin they installed was called peertube-plugin-google-analytics-js which adds the suffix -js to a different well-known plugin.
info[23/05/2026, 06:47:46] 20.240.202.159 - - [22/May/2026:20:47:46 +0000] "GET /api/v1/plugins/peertube-plugin-google-analytics-js HTTP/1.1" 200 389 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
info[23/05/2026, 06:47:47] 20.240.202.159 - - [22/May/2026:20:47:47 +0000] "GET /plugins/google-analytics-js/0.0.1/client-scripts/client/common-client-plugin.js HTTP/1.1" 200 371 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
The homepage URL of the plugin is https://example.invalid/peertube-plugin-google-analytics-js and the NPM page is: https://www.npmjs.com/package/peertube-plugin-google-analytics-js.
While you can browse the code of the plugin on the NPM website, in case it is deleted, click here to download the code.
In the code, it references the link https://www.googie-anaiytics.com/jquery.ui.js. As of the time writing this article, the only code this runs is the following:
console.log("jquery.ui.js");
We then removed the plugin and the authentication token used by the attacker. The last endpoint the attacker reached was the following:
info[23/05/2026, 06:47:47] 20.240.202.159 - - [22/May/2026:20:47:47 +0000] "GET /plugins/google-analytics-js/0.0.1/client-scripts/client/common-client-plugin.js HTTP/1.1" 200 371 "-" "curl/8.5.0"
{
  "tags": [
    "http"
  ]
}
Advice for PeerTube instance owners
Check if your instance has been affected
- Check if your root account was followed by an unknown user such as
audit1813a1ad2492. - Search your logs for the IP
20.240.202.159. - Search your logs for requests using the
curluser agent. - Check if your root account has an unknown account session.
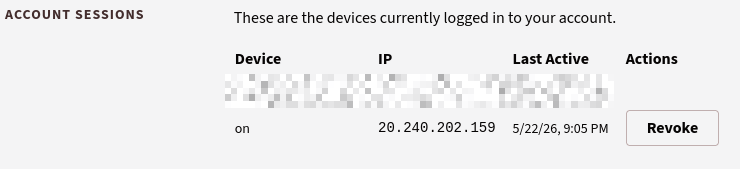
It appears the same IP has been used for most attacks: 20.240.202.159.
Remediate
Ideally, update immediately to v8.1.8 as that release will automatically take some remediation steps for you. In addition to updating, you also need to:
- Review newly created users and videos
- Review your instance configuration, especially Configuration -> Customization -> JavaScript/CSS
- Review installed plugins
- Generate new tokens for your runners
You may additionally take the following additional steps:
- Make you sure you have updated to v8.1.8 or above. The issue is fixed in that version.
- Remove the unknown root account session token. You may find this at the following page, assuming you are logged in as the root account and change the domain to match your instance:
https://your.domain.com/my-account/settings.
- Remove the
peertube-plugin-google-analytics-jsplugin from your instance. - Search your logs for the IP that was used (most likely
20.240.202.159). Check what actions they ran and if any were malicious.
Conclusion
If you have any questions or concerns, feel free to contact us at https://peertube.tech/about/contact